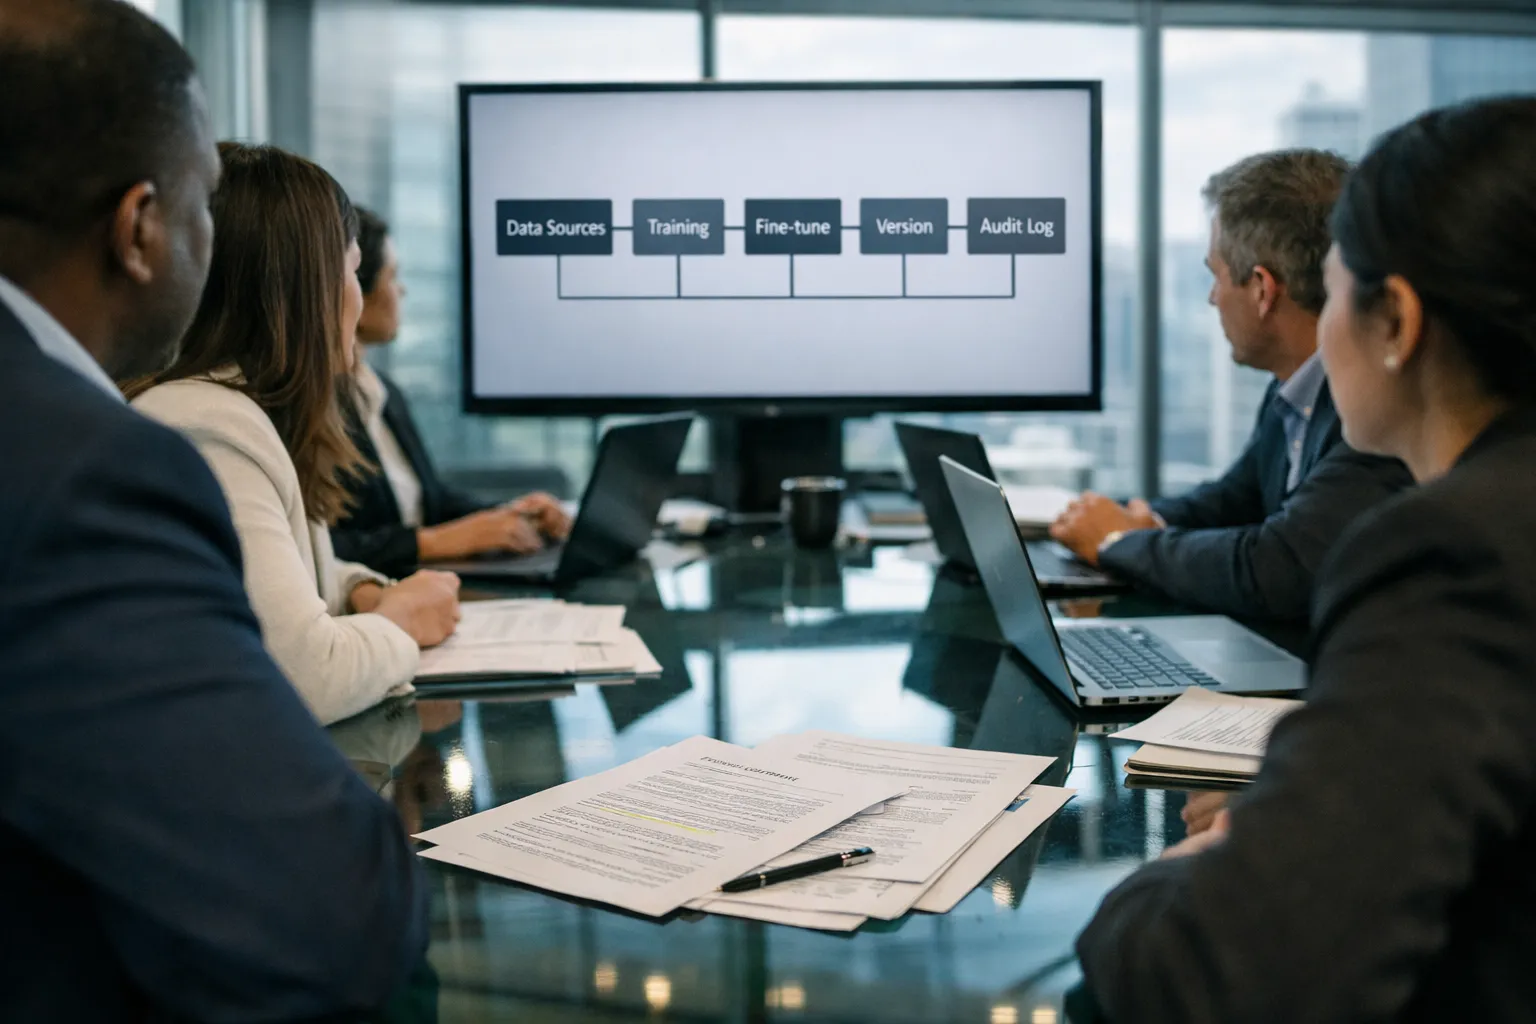
Who: enterprise procurement, legal, security and ML‑ops teams buying third‑party models; What: updated best practices and contract language for "model provenance"; When: November 2026; Where: global, with concentration in regulated sectors (finance, healthcare, public sector); Why: to satisfy auditors, respond to supervisory expectations and reduce AI supply‑chain risk as provenance tooling and verification services mature.
Context — why provenance clauses moved from optional to routine
By late 2026, model provenance is no longer an optional clause in enterprise AI procurements. The shift that began with pilots in 2023–2024 accelerated through 2025–2026 as three linked forces converged:
- Regulatory and supervisory pressure: Supervisors across the EU and the UK continue to treat lineage, documentation and reproducible evidence as core supervisory artifacts for high‑risk AI. Buyers report that regulators routinely request a model card, signed chain‑of‑custody and evaluation artifacts during examinations.
- Platform and marketplace support: Major cloud and marketplace vendors — including AWS, Microsoft Azure, Google Cloud and Hugging Face — now embed machine‑readable metadata endpoints, signed artifact bundles and APIs that export provenance into enterprise registries, reducing manual integration work for buyers.
- Verification and neutral services: A market of independent validators, neutral logging providers and technical escrow firms has emerged. These providers routinely offer tamper‑evident logs (often using content‑addressable storage and cryptographic signatures), normalization adapters and controlled forensic review services for high‑risk contracts.
What November 2026 provenance clauses now require
Contract language has continued to standardize around a pragmatic, machine‑readable set of deliverables that enterprise buyers use as gating items for production deployment:
- Persistent identifiers and signed chain‑of‑custody: UUIDs or content hashes for model artifacts and derivative versions; a signed manifest listing developers, training and packaging environments, build tools and timestamps.
- Data and training lineage assertions: Machine‑readable statements classifying training data by origin (licensed, public, customer, synthetic), dataset versions and transformations. Where full dataset disclosure is restricted, vendors supply indexable provenance pointers and granular attestations under NDA or in escrow.
- Evaluation, performance and fairness artifacts: Timestamped model cards, evaluation reports, adversarial‑test outputs and configuration metadata in JSON/JSON‑LD to support reproducibility and supervisory review.
- Operational telemetry and tamper‑evident logs: Contracted access to deployment logs, drift reports and a signed event stream or neutral logging feed that records behavior‑affecting updates, security patches and deprecations.
- Retention, export and audit rights: Explicit retention windows (36 months remains common for high‑risk models), export rights to support regulator requests, and procedures for emergency escrow access.
- Attestation and independent verification: Vendor attestations of artifact accuracy plus contractual provisions for third‑party validation, with defined scope, frequencies and cost‑sharing for forensic reviews.
New practical developments since September 2026
- Normalization as a service: The last quarter saw a wider availability of vendor‑agnostic normalization adapters that map diverse vendor metadata into enterprise schemas (for example, model registries and GRC platforms). That has materially reduced per‑vendor integration time for many buyers.
- Automated gating in CI/CD: More enterprises now enforce provenance gates in CI/CD pipelines for model promotion: a model must present a valid signed bundle and pass schema validation before moving to staging or production.
- Neutral logging commercialization: Neutral logging services offering independent, tamper‑evident event streams have become a standard option in RFPs for very high‑risk deployments, removing single‑vendor trust assumptions.
- Cost profiling: Buyers increasingly treat verification and escrow as line items. Typical market ranges observed across procurement teams in 2026: lightweight attestations and schema validation commonly cost hundreds to low thousands of dollars; deep forensic verification, escrow setup or dataset re‑creation estimates typically range from $20,000 to $150,000 depending on compute and data access needs.
How enterprises are operationalizing provenance
- Procurement teams require signed provenance bundles and API access as a precondition for adding vendor models to enterprise model registries.
- Security and ML‑ops ingest vendor metadata into registries (ServiceNow, Collibra, proprietary registries or MLflow integrations), linking artifacts to asset IDs, SLAs and incident‑response playbooks.
- Internal audit and compliance use normalized provenance artifacts for targeted sampling. Many teams report audit time for sampling and evidence collection has fallen, enabling more frequent checks without proportional staffing increases.
- Operations tie provenance triggers to SRE and incident‑response runbooks: signed behavior‑altering events in logs can automatically create high‑priority incidents and start contractual remediation timelines.
Market and vendor playbooks — how suppliers balance transparency and IP
- Layered disclosure: public machine‑readable summaries (model cards and evaluation snapshots), controlled disclosure under NDA or escrow for full manifests, and escrowed forensic access for the highest‑risk cases.
- Cryptographic signing and CAS: many vendors publish signed metadata bundles and store artifacts in content‑addressable storage, making tampering evident and enabling quicker validation checks.
- Service tiers: vendors now offer provenance tiers — standard metadata endpoints for general use, enhanced attestations with neutral logging for regulated customers, and full‑forensic options priced separately.
Remaining challenges and tradeoffs
- Schema fragmentation: Multiple competing metadata formats remain. Normalization layers reduce friction but add cost and governance overhead.
- Proprietary pipeline limits: Vendors often limit low‑level pipeline access. Buyers must exercise risk‑based negotiation or accept attestation plus third‑party verification.
- Cost and procurement complexity: Escrow, cryptographic infrastructures and deep verification increase procurement complexity and require clear thresholds for when to require extra assurance.
Updated practical next steps for buyers (November 2026)
- Mandate a minimum, machine‑readable provenance package as a contract precondition: persistent model identifier, model card (JSON/JSON‑LD), evaluation artifacts and a signed chain‑of‑custody manifest.
- Define retention and export rights aligned to regulatory needs — for example, 36 months for high‑risk models; document shorter windows for non‑critical models.
- Deploy a normalization layer (a model registry or adapter) to ingest vendor metadata into enterprise taxonomies; use third‑party adapters where available to reduce vendor‑specific mapping overhead.
- Operationalize automated provenance gating in CI/CD pipelines to prevent promotion without valid signed artifacts and schema validation.
- Budget for periodic independent verification for models that affect safety, fairness or regulated outcomes; specify scope, frequency and cost‑sharing in contracts.
- Include escalation matrices that map provenance triggers (unexpected drift, bias flags, signed behavior‑altering updates) to contractual remedies: mandatory patch windows, rollback rights or escrow retrieval.
Impact — who this affects and why it matters
Standardized provenance reduces time‑to‑remediate incidents, strengthens supervisory responses and lowers regulatory friction. The benefits are greatest in regulated sectors — financial services, healthcare, public procurement — but matter equally to any company relying on third‑party models for mission‑critical services, customer interactions or compliance‑sensitive decisions.
Reactions from the field
Procurement and compliance leaders report that provenance clauses are now standard in RFPs for high‑risk AI. Vendor product and cloud teams point to customer demand for signed metadata endpoints and neutral logging. Independent validators note rising demand for cryptographic attestations and escrow arrangements, especially among buyers operating across multiple regulatory jurisdictions.
What's next — what to watch through 2027
- Further schema convergence: expect continued working‑group momentum toward interoperable JSON/JSON‑LD patterns; normalization adapters will bridge the gap in the meantime.
- Regulatory clarification: supervisors are likely to publish more granular expectations for provenance artifacts as part of routine AI examinations.
- Commercialization of neutral attestation services: a broader market of vendor‑agnostic logging, escrow and verification offerings should lower friction and cost for buyers.
- Insurance and liability: provenance artifacts will play a growing role in underwriting and incident attribution for model liability insurance products.
Can provenance clauses alone satisfy regulators?
Provenance clauses supply necessary evidence — signed model metadata, evaluation artifacts and tamper‑evident logs — but they are not sufficient on their own. Regulators expect governance processes, incident‑response playbooks, continuous monitoring and demonstrable operational controls in addition to provenance artifacts.
How much should buyers budget for verification?
Costs vary by depth. Lightweight attestations and schema validation commonly cost in the low hundreds to a few thousand dollars per validation. Deep forensic verification and escrow retrieval can range from roughly $20,000 to $150,000 depending on compute, data access and specialist time. Define thresholds and cost‑sharing up front.
What leverage do buyers have if vendors refuse deep disclosure?
Options include: (1) rejecting the vendor for high‑risk use cases, (2) accepting the vendor with enhanced contractual mitigations (restricted scope of use, stronger monitoring), or (3) requiring escrowed artifacts and independent attestation as conditions of production deployment.
How should buyers handle cross‑border constraints?
Include explicit export and disclosure clauses that account for data‑transfer rules and regulator access. Retain machine‑readable artifacts locally where possible and use neutral escrow or independent validators to bridge jurisdictional constraints while preserving confidentiality.
What immediate checklist should a buyer use in November 2026?
A short operational checklist: (1) require a signed provenance bundle and API access in RFPs, (2) validate schema compliance in pre‑production CI gates, (3) map provenance artifacts to regulatory evidence requirements, (4) budget for independent validation for top‑risk models, and (5) codify escalation and rollback rights in contracts.