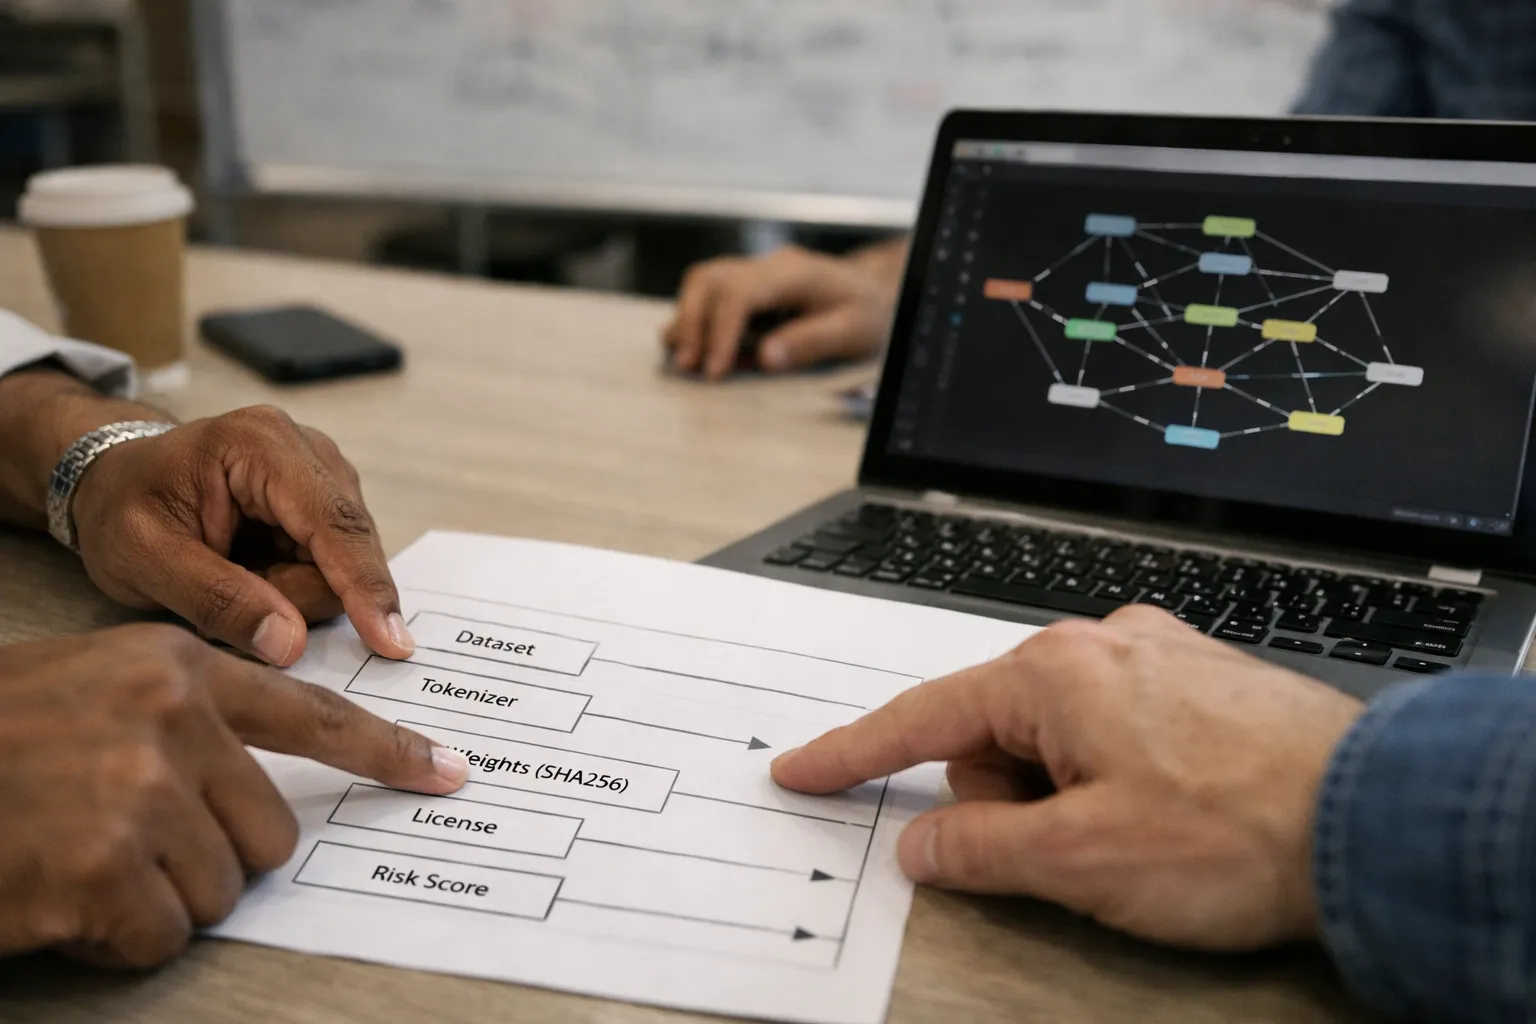
Enterprise AI teams, procurement leaders and security officers are increasingly discussing a practical instrument that could change how organizations buy, operate and audit machine learning models: a Model Bill of Materials (MBOM), often described as an “ML SBOM.” Rather than a single product launch, the movement represents a set of converging practices and pilot projects that aim to make model provenance, data lineage, licensing and component risk explicit and machine-readable.
What an MBOM would do for enterprise AI
An MBOM mirrors the software bill of materials used in software supply chains but is tailored to the unique composition of machine learning systems. At minimum, an MBOM would capture:
- Model identity and versioning: model architecture, weights checksum, training configuration.
- Data provenance: dataset identifiers, sources, sampling procedures, and preprocessing pipelines.
- Third-party components: libraries, pretrained embeddings, tokenizers, vector stores and any external APIs invoked during inference.
- Licensing and contractual constraints: usage rights, export controls, and downstream use restrictions.
- Risk and compliance metadata: known biases, safety test results, red-team outcomes and model risk scorecards.
- Reproducibility artifacts: training scripts, random seeds, hardware details and environment manifests.
Captured in a standard, machine-readable MBOM, these items would let procurement, security and legal teams automate checks at contract time, enable continuous monitoring in production, and accelerate incident response when models behave unexpectedly.
Why the push is gaining traction now
Three practical shifts have accelerated interest in an MBOM:
- Compositional complexity: Modern production AI systems are assemblies of datasets, open-source and closed-source model components, cloud services and vector stores. Visibility gaps create procurement and operational blind spots.
- Regulatory pressure and governance needs: Even where formal regulation is still evolving, enterprise risk teams require evidence trails for vendor due diligence, auditability and consumer complaints.
- Operational reproducibility and incident response: When a model generates a damaging output or degrades, teams need a fast way to identify which dataset, preprocessing step or external dependency is implicated.
How MBOMs differ from existing artifacts
Enterprises already use model cards, datasheets and metadata stores; an MBOM is intended to be a practical bridge between those descriptive artifacts and operational governance:
- Model cards explain intended use and limitations; MBOMs record the full dependency graph and legal constraints in a standardized schema.
- Data lineage tools show how a dataset was transformed; MBOMs link those lineage traces with the specific model versions that consumed them.
- Artifact registries and metadata stores keep per-artifact info; MBOMs bundle relevant artifacts into a single manifest suitable for contract exchanges and automated checks.
Enterprise use cases
Practical, near-term uses for MBOMs in enterprises include:
- Automated procurement checks: Vendors can attach an MBOM to a model SKU so buyers can programmatically verify licensing compatibility, export-control flags and data usage constraints before purchase.
- Continuous compliance monitoring: Security and risk platforms can ingest MBOMs to detect when an upstream dependency receives a CVE or license change that affects deployed models.
- Faster incident triage: With an MBOM, SRE and ML engineers can immediately see the exact dataset and preprocessing pipeline used for a problematic prediction, shortening MTTR.
- Standardized vendor liability: MBOMs could become part of contractual SLAs, clarifying what components are covered under vendor support and what remains the buyer’s responsibility.
Technical and organizational hurdles
Adopting an MBOM is not simply a technical integration. Key challenges include:
- Standard schema and tooling: Organizations need a common format and APIs so MBOMs are consumable across registries, MLOps platforms and procurement systems.
- Provenance verification: Checksums and cryptographic signing help, but pipelines that mix third-party and proprietary components complicate authenticity guarantees.
- Commercial sensitivity: Vendors resist exposing details that they consider trade secrets; MBOMs must balance transparency with IP protection.
- Data privacy and security: MBOMs may reference sensitive dataset identifiers and require access controls to avoid leaking customer or personal data.
What enterprises should do now
Teams planning to adopt MBOM practices can take concrete steps immediately:
- Inventory model assets and dependencies in a central registry and start capturing minimal provenance (checksums, model version, dataset ID).
- Integrate MBOM thinking into procurement docs: require vendors to disclose a dependency manifest at RFP time and flag licensing constraints.
- Pilot MBOM consumption with one high-risk use case — for example, a customer-facing chatbot or an automated underwriting model — to validate workflows and tooling.
- Contribute to or monitor developing open schemas and community projects to avoid vendor lock-in and to adopt interoperable formats as they stabilize.
Why MBOMs matter for the AI-for-business landscape
As enterprises scale AI, the need for standardized, automated visibility into what’s inside a model mirrors the trajectory that software underwent with SBOMs. An MBOM will not solve all governance problems, but it can materially reduce friction across procurement, legal, security and engineering by making model composition explicit. For organizations investing heavily in AI, that clarity is rapidly moving from a “nice to have” to a practical necessity.
Expect early MBOM pilots to focus on regulated industries — finance, healthcare and critical infrastructure — where auditability and traceability already factor into vendor selection. Over time, the community — open-source projects, MLOps vendors, procurement consortia and standards bodies — will determine whether an MBOM becomes a de facto enterprise requirement or a purpose-limited tool used for high-risk models.