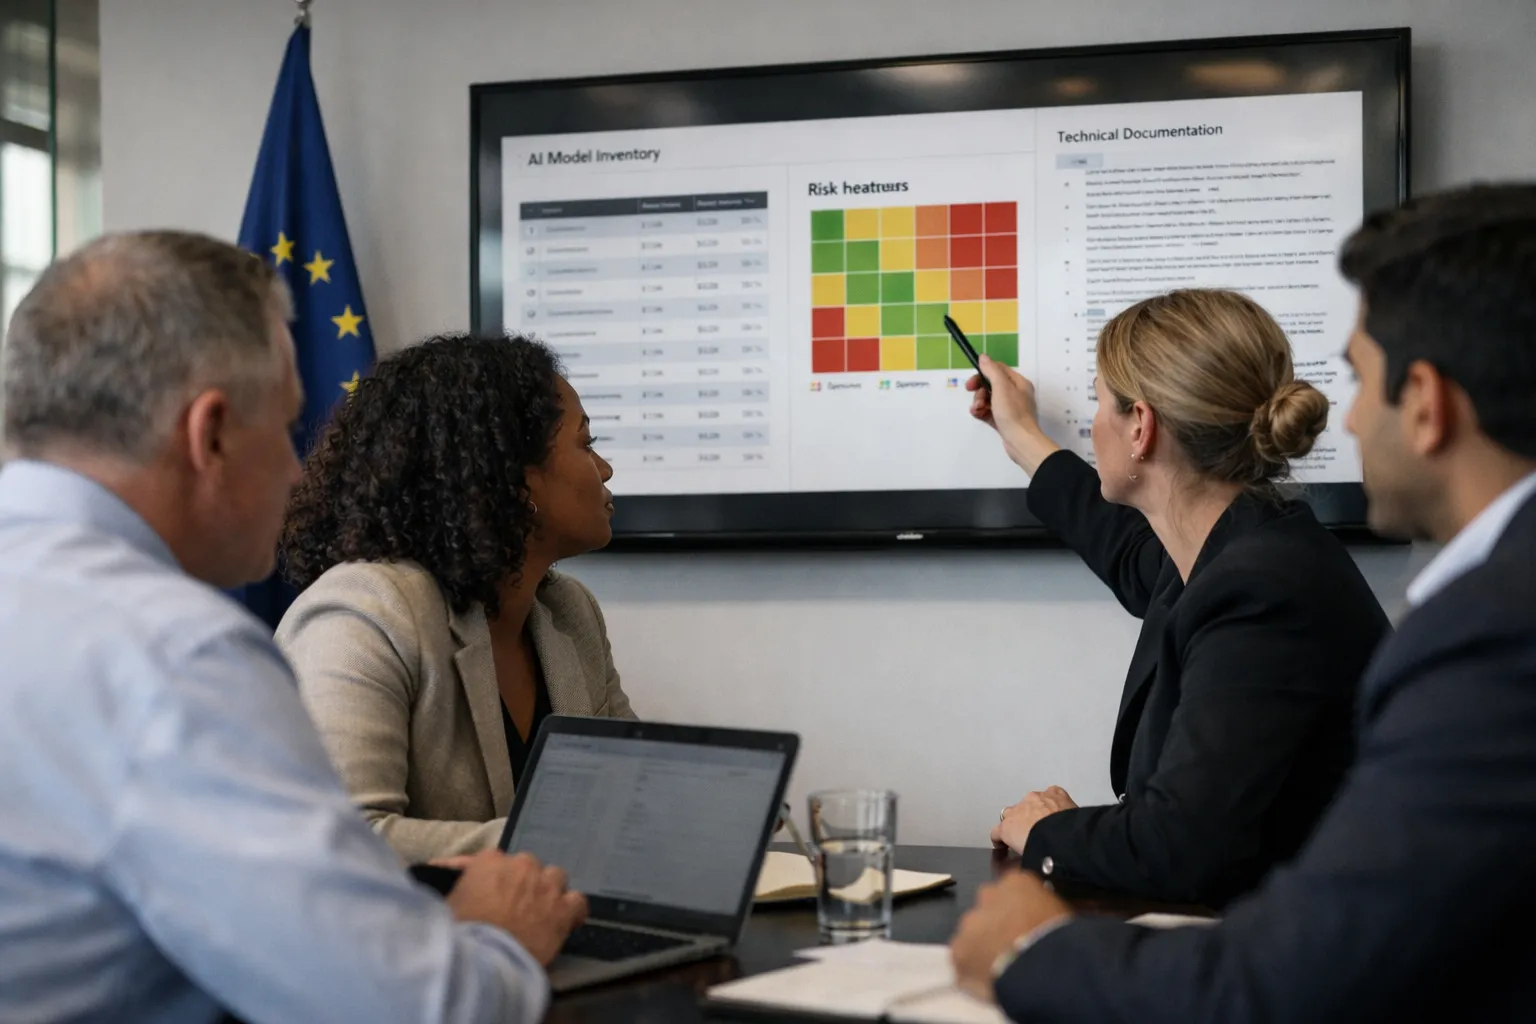
Brussels — As the EU's landmark AI regulation transitions into active enforcement in 2026, enterprise teams that deploy large language models (LLMs) are scrambling to close compliance gaps. The law's focus on high‑risk AI systems — and its requirements for documentation, risk management and post‑market monitoring — is forcing procurement, legal and engineering teams to coordinate on new processes, tooling and vendor contracts.
What the regulation requires for enterprise LLMs
The European Union's AI Act identifies a category of high‑risk systems that are subject to stricter controls. For enterprises, that translates into several concrete obligations when LLMs are used in regulated contexts (hiring, lending, legal advice, medical triage, critical infrastructure, and certain public services):
- Risk management systems: documented processes to identify, assess and mitigate risks across the model lifecycle.
- Technical documentation: model cards, training data summaries, evaluation results and development records that are maintained and made available to competent authorities on request.
- Human oversight: controls and workflows ensuring meaningful human review for automated decisions that materially affect individuals.
- Transparency and information provision: users must receive clear information about AI-driven decisioning, including limitations and intended use.
- Post‑market monitoring and incident reporting: continuous monitoring of deployed models and duties to report serious incidents or malfunctions.
- Conformity assessment: in many cases, providers and deployers must complete internal checks or third‑party audits and be able to demonstrate compliance.
Why LLMs are squarely in regulators' sights
LLMs power a wide range of enterprise applications that touch regulated sectors: automated customer support that influences credit and service eligibility, internal tools that summarize employee performance, and external‑facing assistants that generate legal or financial guidance. The scale and autonomy of these models — together with their propensity to hallucinate, reveal training data, or replicate biases — make them a clear target for the EU's risk‑based approach.
How vendors and enterprises are responding
Cloud vendors, AI platform providers and a wave of governance startups have accelerated product changes and feature launches to help customers meet the Act's documentation and monitoring requirements. Emerging vendor offerings include:
- Automated model inventory and lineage tools that track model versions, data sources and deployment contexts across multi‑cloud footprints.
- Built‑in logging and tamper‑resistant audit trails for inputs, outputs and mitigation actions.
- Prepackaged “conformity kits” with template technical documentation, evaluation suites and guidance for third‑party audits.
- Human‑in‑the‑loop controls and configurable risk thresholds to enforce oversight on high‑impact flows.
Procurement teams report that vendors are now including compliance clauses in standard contracts and offering certified deployment modes or add‑ons that restrict model capabilities to documented, auditable behaviors.
Costs and operational impact
Compliance is not only a legal exercise; it has measurable operational costs. Companies must staff cross‑functional risk reviews, expand logging infrastructure, and invest in continuous evaluation pipelines. Early adopters say the largest near‑term costs are:
- Engineering time to integrate logging, access controls and monitoring into production LLM pipelines.
- Legal and compliance overhead to map AI use cases to regulatory expectations and to update vendor contracts.
- Third‑party audit fees and internal spend on external consultants for conformity assessments.
Practical checklist for enterprise AI leaders
AI leads and CTOs should prioritize the following steps to reduce regulatory and business risk:
- Inventory deployments: build a centralized register of all LLMs and generative AI use cases, with owners and risk ratings.
- Classify risk: map each deployment to regulated activities to determine whether it falls under high‑risk obligations.
- Document the pipeline: maintain technical documentation, training data summaries and evaluation artifacts for each model version.
- Establish human oversight: design intervention points and escalation processes for decisions with material impact.
- Enable observability: implement robust logging, monitoring and anomaly detection for model behavior in production.
- Contract clarity: require SLAs and compliance warranties from vendors, and ensure rights to audit and access provenance information.
- Plan for audits: run internal conformity checks and prepare for external assessments where required.
Legal exposure and enforcement risks
Non‑compliance can lead to fines and restricted deployment in the EU market. The Act introduces proportionate penalties for serious breaches, and regulators have powers to demand corrective measures. Beyond fines, enterprises face reputational damage and potential contractual liabilities if AI systems cause harm or discriminate.
Looking ahead: standardization and market implications
Over the next 12–18 months, expect greater standardization of compliance tooling and the emergence of industry‑specific conformity frameworks. Enterprises that invest early in model governance may gain competitive advantage: they will be able to demonstrate safer, auditable AI practices to customers and regulators while minimizing disruption to product roadmaps.
For AI leaders, the core strategic choice is whether to treat compliance as a checklist or as an integrated capability. Those who build governance into the engineering lifecycle — automated documentation, continuous evaluation and clear human oversight — will be better positioned to scale generative AI responsibly in regulated contexts.
As enforcement accelerates in 2026, enterprises that delay will face higher remediation costs, constrained deployments and increased regulatory scrutiny. The time for cross‑functional action is now.