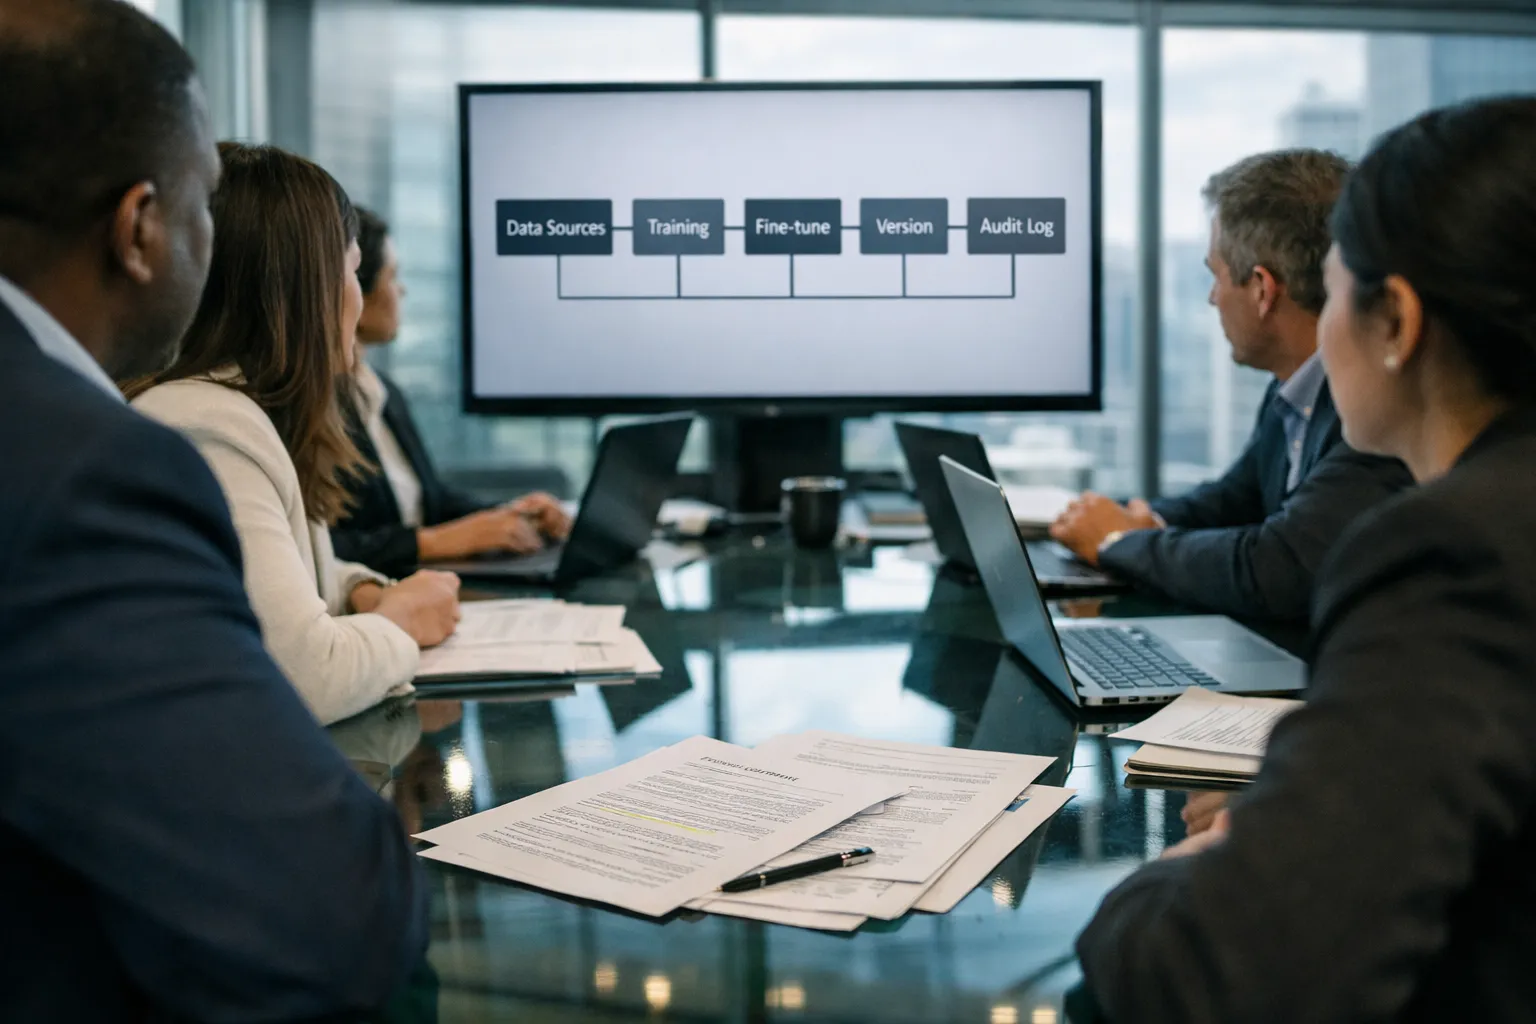
Who: Enterprise procurement, legal, security and ML‑ops teams buying third‑party models; What: standardizing and operationalizing "model provenance" contract clauses; When: June 2026; Where: global deployments across regulated sectors (finance, healthcare, public sector); Why: to satisfy auditors, comply with regulation and reduce AI supply‑chain risk.
Why provenance clauses have moved from optional to routine — June 2026
Since the first wave of provenance contract pilots in 2023–2024, three forces have accelerated adoption through the first half of 2026.
- Regulatory and supervisory pressure: Regulators in the EU, United Kingdom and several national supervisory authorities now treat model lineage and documentation as core supervisory evidence in high‑risk AI use cases. The EU AI Act's classification of systems as "high‑risk" and supervisory guidance published in 2025 have been particularly influential for cross‑border procurement in regulated industries.
- Platform‑level support: Major cloud providers and model marketplaces—including AWS, Microsoft Azure, Google Cloud and Hugging Face—now provide out‑of‑the‑box, machine‑readable provenance bundles (metadata, model cards, evaluation artifacts) and APIs to export them into enterprise registries, reducing integration cost for buyers.
- Emergence of verification services: A growing market of third‑party validators and "provenance attestations" has reduced verification friction. Independent validators now commonly offer cryptographic attestation, tamper‑evident logs and escrowed artifacts for sensitive contracts.
What modern model‑provenance clauses require (2026 practical template)
Contract language has converged around a practical, machine‑readable set of artifacts. Buyers routinely require the following items as contract deliverables and gating items for production use.
- Unique model and component identifiers: Persistent identifiers (for example, UUIDs or content‑addressable hashes) for the model and each derivative version, plus a signed chain of custody listing developers, training environments and packaging tools.
- Training and data lineage assertions: Machine‑readable statements identifying data sources by category (licensed, public, customer‑provided, synthetic), dataset versions, and any data‑transformation or augmentation pipelines. Where full dataset disclosure is impractical, vendors provide granular attestations and indexable provenance pointers under confidentiality protections.
- Performance, evaluation and fairness artifacts: Timestamped model cards, evaluation reports, test harness outputs and adversarial‑test results in standardized JSON or JSON‑LD formats that include configuration and random seed metadata required for reproducibility claims.
- Operational telemetry and tamper‑evident logs: Contracted access to deployment logs, drift reports, and a tamper‑evident event stream (signed by the vendor or delivered via a neutral logging service) documenting behavior‑affecting updates, security patches and deprecations.
- Retention, export and audit rights: Buyer rights to retain copies of provenance artifacts for defined retention periods (commonly 36 months for high‑risk models), with export rights for regulators and independent auditors, and procedures for emergency escrow access.
- Attestation and third‑party verification: Vendor attestation of artifact accuracy plus contractual mechanisms for independent validation, including a defined scope, frequencies and cost‑sharing rules for deep verification (for example, forensic access to training environments under a controlled review).
How enterprises are implementing provenance in production
The implementation model in 2026 is hybrid: contract language sets minimum obligations and cloud/platform features plus internal controls operationalize enforcement.
- Procurement teams make signed provenance bundles and API access a contractual precondition for submission to enterprise model registries.
- Security and ML‑ops ingest provider metadata into internal model registries (for example, ServiceNow, Collibra, or bespoke registries), linking vendor artifacts to asset IDs, SLA terms and incident‑response playbooks.
- Internal audit and compliance rely on normalized provenance artifacts for targeted sampling rather than re‑creating full training histories, reducing audit overhead by as much as half in internal pilots.
New case usages enabled by mature provenance
As provenance artifacts become machine‑readable and standardized, enterprises can:
- Automatically map a production bias alert to a specific training dataset version and vendor component within minutes rather than days.
- Trigger contractual remediation clauses—automatic rollback, targeted patches, or escrow retrieval—based on signed event logs that show a behavior‑altering update.
- Provide regulators with standardized export packages (model card + evaluation artifacts + signed chain of custody) that satisfy supervisory evidence requests during investigations.
Market responses and vendor playbooks in 2026
Vendors balance transparency and IP protection with layered disclosure models that have become mainstream:
- Public, machine‑readable summaries (model cards, evaluation snapshots) available in metadata endpoints for everyday audits.
- Controlled disclosure under NDAs or technical escrow for full training manifests and dataset indexes in high‑risk deployments.
- Integration of cryptographic signing for provenance artifacts: several vendors publish signed metadata bundles and use content‑addressable storage (CAS) to make artifacts tamper‑evident.
Third‑party providers now offer normalization adapters that transform vendor metadata into common schemas used by enterprise governance tools. Open‑source initiatives and industry consortia working on metadata standards—in particular communities around MLCommons and ISO/IEC SC‑42 working groups—have accelerated convergence, though a single global schema has not fully emerged.
Remaining challenges and risk tradeoffs
Despite progress, notable hurdles remain:
- Schema fragmentation: Multiple competing schemas (vendor‑specific JSON schemas, JSON‑LD model cards, and emerging industry formats) require mapping layers and increase integration cost.
- Proprietary pipeline limits: Vendors still limit access to low‑level pipeline artifacts; buyers must negotiate deeper access only for the riskiest models or accept attestation plus third‑party verification.
- Cost and governance: Third‑party verification, escrow arrangements and cryptographic infrastructure raise procurement and operational costs; buyers need clear risk‑based thresholds to decide when to pay for deeper verification.
Updated practical next steps for buyers (June 2026)
Procurement, legal and risk teams should treat provenance as an enforceable control with measurable gates:
- Mandate a minimum, machine‑readable provenance package as a contract precondition: model identifier, model card (JSON), evaluation artifacts (JSON), and signed chain‑of‑custody manifest.
- Define retention periods and export rights aligned to regulatory needs—e.g., 36 months for high‑risk models; shorter for non‑critical utilities.
- Deploy a normalization layer (model registry) to ingest and map vendor metadata to enterprise taxonomies and compliance checklists; use adapters from trusted third‑party vendors where available.
- Build an escalation matrix that ties specific provenance triggers (unexpected drift, bias flags, behavior‑altering updates) to contractual remedies: mandatory patch windows, rollback rights, or escrow retrieval.
- Budget for periodic independent verification for models that affect safety, fairness or regulated outcomes; define scope and cost‑sharing in contracts.
Impact — who this affects and why it matters
Standardized provenance reduces time‑to‑remediate for incidents, strengthens audit responses, and lowers regulatory friction. It disproportionately benefits regulated sectors—financial services, healthcare, public procurement—but also helps technology and retail firms that rely on third‑party models for mission‑critical services.
Reactions from the field
Procurement and compliance leaders report that provenance requirements are now a routine part of RFPs for high‑risk AI. Cloud and vendor product teams say customer demand drove new metadata APIs and signed artifacts in 2025. Independent validators report growing demand for cryptographic attestations and escrow services, particularly from European and North American buyers.
What's next — what to watch through the rest of 2026
- Further convergence on metadata schemas: look for working group publications from ISO/IEC SC‑42 and industry consortia in late 2026 that aim to harmonize JSON‑LD patterns for provenance.
- Regulatory clarification: expect more detailed supervisory guidance from financial and healthcare regulators specifying minimal provenance artifacts for compliance evidence.
- Market standard services: anticipate expanded offerings for neutral logging/attestation services and vendor‑agnostic normalization adapters that reduce integration overhead.
Can provenance clauses satisfy regulators?
Provenance clauses are necessary but not sufficient. They supply core evidence—signed model metadata, evaluation artifacts and tamper‑evident logs—that regulators typically request. Organizations still need governance processes, incident‑response playbooks and evidence of operational controls to demonstrate effective oversight.
What level of detail should buyers demand from vendors?
Use a risk‑based approach. Require full technical artifacts and forensic access for high‑risk models; require standardized metadata, signed model cards and behavioral test results for medium‑risk models; and accept lighter summaries for low‑risk utilities. Specify scope, access methods and cost sharing in the contract.
How much does third‑party verification cost?
Costs vary by depth: lightweight attestations and schema validation can be low hundreds to a few thousand dollars per audit; deep forensic verification and escrow retrieval can run tens of thousands depending on compute and data‑access needs. Define thresholds and cost‑sharing up front.
If vendors refuse deep disclosure, what leverage do buyers have?
Buyers can: (1) reject the vendor in procurement for high‑risk use cases, (2) accept the vendor with additional contractual mitigations (e.g., enhanced monitoring, constrained scope of use), or (3) require escrowed artifacts and independent attestation as a condition of production deployment.
How do enterprises prove provenance in cross‑border environments?
Include explicit export and disclosure clauses that account for cross‑border data transfer rules and regulator access. Retain machine‑readable artifacts locally where possible, and use escrow or neutral third‑party validators to bridge jurisdictional constraints.